Private beta · Linux servers · EU hosted
You ship it.
Jack watches it.
You built the app with Claude Code or Cursor and pushed it to a VPS. Nobody is looking after that box. Jack is: he reads the threat feeds every hour, checks them against what your servers actually run, and tells you the few things that matter. He never changes anything without your OK.
- feedsCISA KEV, Ubuntu USN, Debian, 6 news feeds. 214 new items.
- match3 servers, 1,912 packages. Distro backports count as fixed.
- skip183 items: not installed on any of your servers.
- skipCVE-2026-40211 nginx: already fixed on web01 and app02.
- flagCVE-2026-31337 openssl on web01. Exploited in the wild.
- jackOne package update fixes it. Want me to queue it? You approve, I run nothing before that.
01What Jack does
-
Watches your servers
OS, packages, services, containers, open ports, certificates, disks, backups. A fresh look every 15 minutes, so he knows what each box runs today, not what you think it runs.
-
Reads the threat feeds
CISA's exploited list, Ubuntu and Debian security notices, security news and Hacker News. All of it, every hour, so you don't have to.
-
Tells you what affects you
Most advisories are about software you don't run. Jack matches on the exact distro version and drops the rest. What's left comes with the fix: usually one update.
-
Asks before he touches anything
The agent is read-only. Jack can suggest a fix and show you exactly what it does. Nothing runs on your server until you approve it.
02Two walls, one glance
Put the Security Wall on a spare screen and you know how the fleet is doing from across the room. The Threat Wall is the feed behind it: every threat that touches your servers, with the server, the package and the version that fixes it.
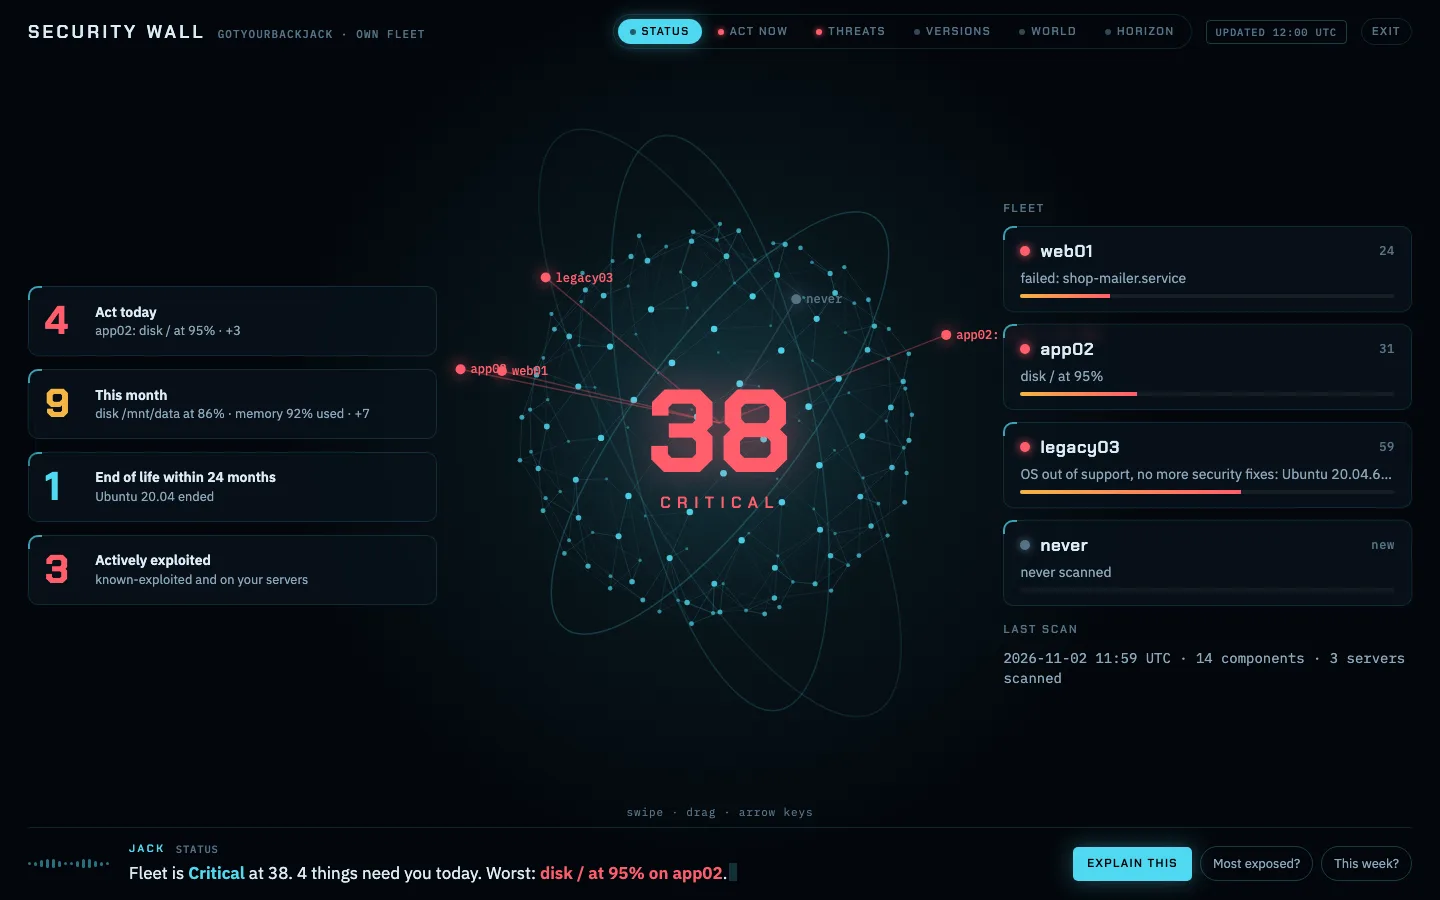
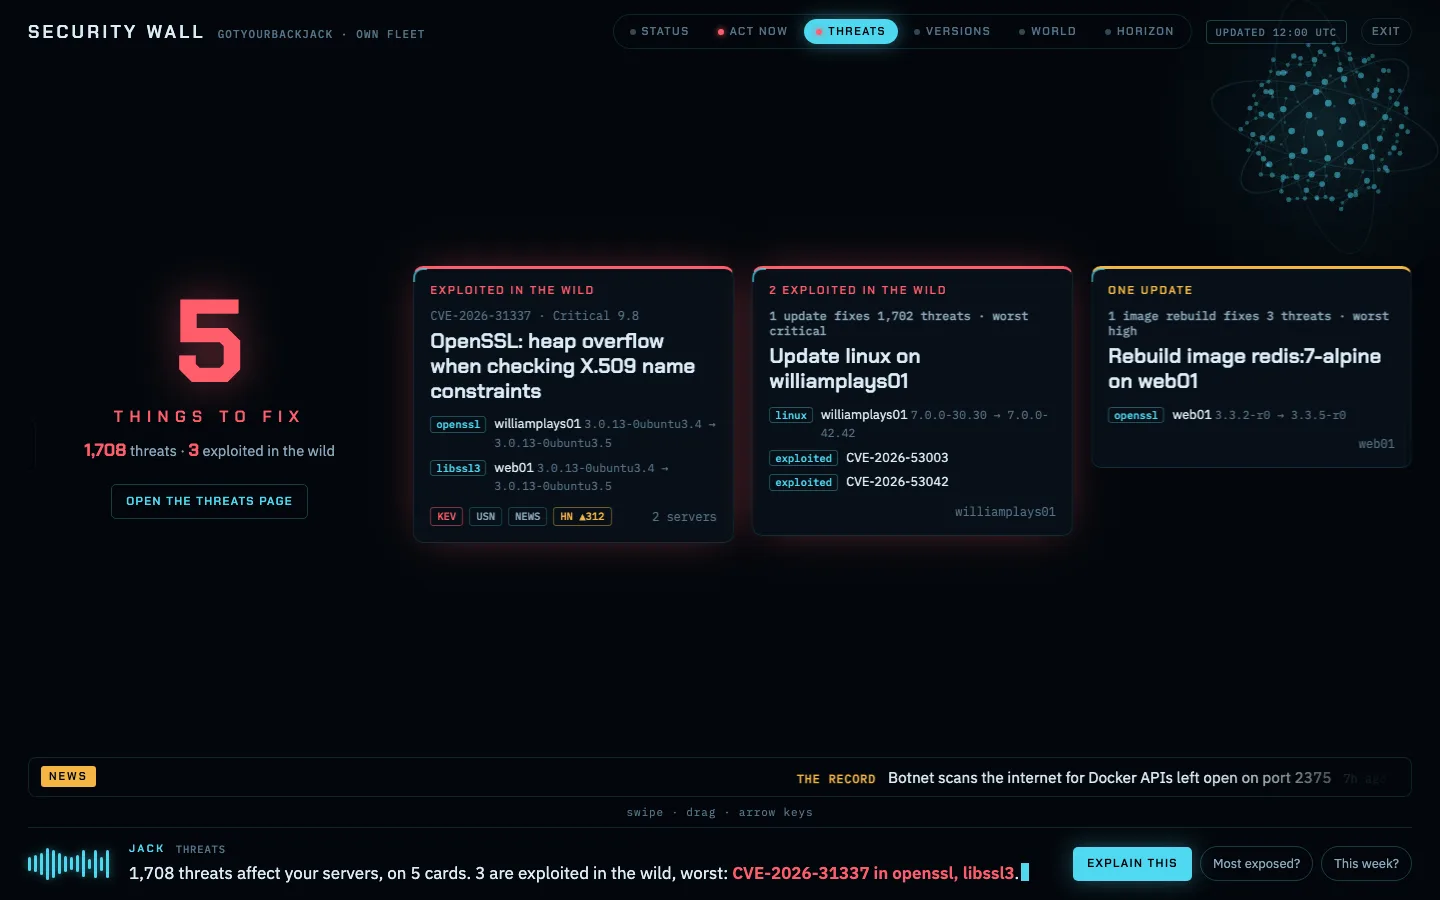
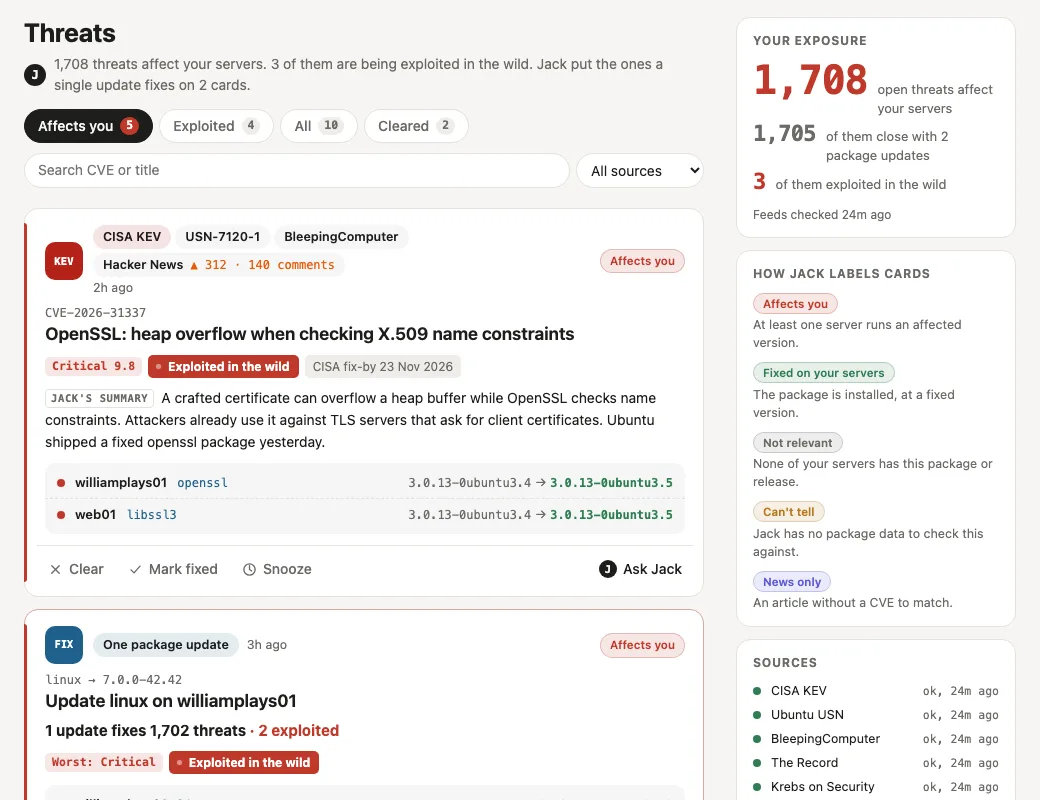
Screenshots from the app with sample data.
03How it works
- Install the agent. One command per server. A small Go binary and one systemd service.
- It reports out. The agent calls Jack over HTTPS. It opens no port and you hand over no SSH keys.
- Jack does the reading. Feeds in, your package lists in, a short list of what matters out: on the wall, by mail or in your coding agent.
$ curl -fsSL https://app.gotyourbackjack.com/install.sh | sh -s -- jet_••••••
- read-only by default
- no listening port
- no SSH keys leave your hands
- hosted in the EU
04Ask Jack from Claude Code
Your coding agent deployed the app, so let it ask about the server too. Jack comes with an MCP server: Claude Code, Cursor and other MCP clients can list your servers, read the threats and request a fix.
Request, not apply. There is no tool that changes a server. A requested fix waits in the app until a person approves it.
> is anything on prod exposed right now?
jack · get_threats server: web01
web01 runs openssl 3.0.13-0ubuntu3.4. CVE-2026-31337 affects it and is being exploited. Ubuntu ships the fix in 3.0.13-0ubuntu3.5.
jack · request_fix update openssl on web01
Requested. It waits in GotYourBackJack until you approve it.
05Private beta
Free while it's a beta.
We are letting in a small group of builders and agencies with real servers in production. Pricing comes later, and you'll hear it before anything costs money.
Tell us what you run and we'll get back to you.